Feature 1
Use task management wherever the work happens
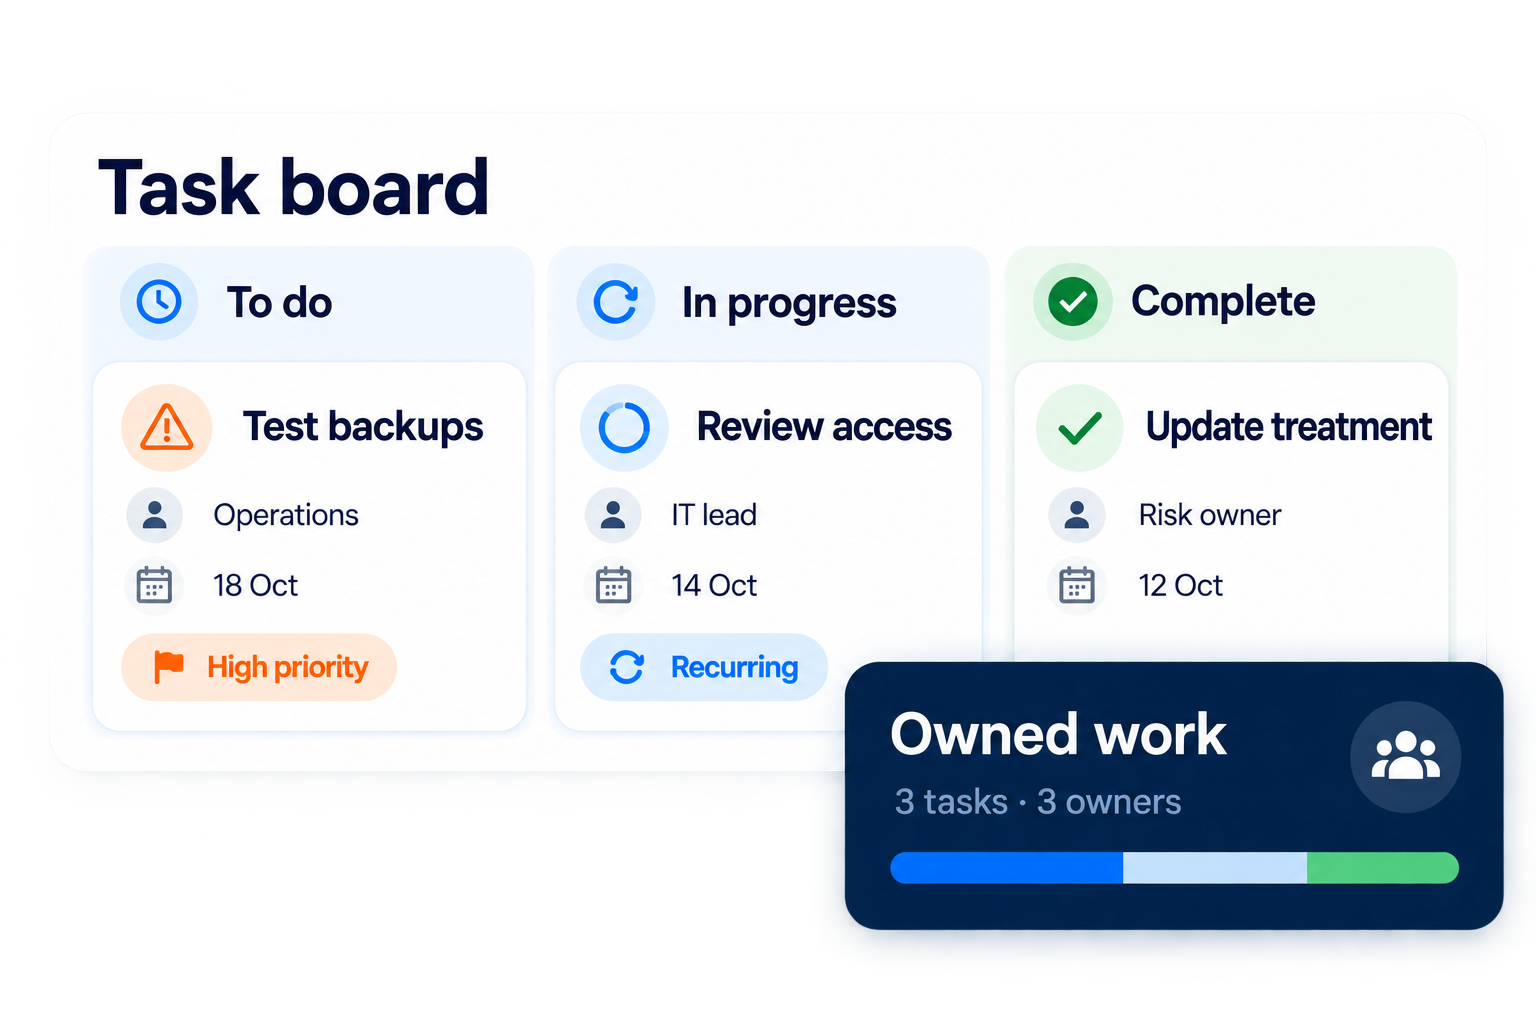
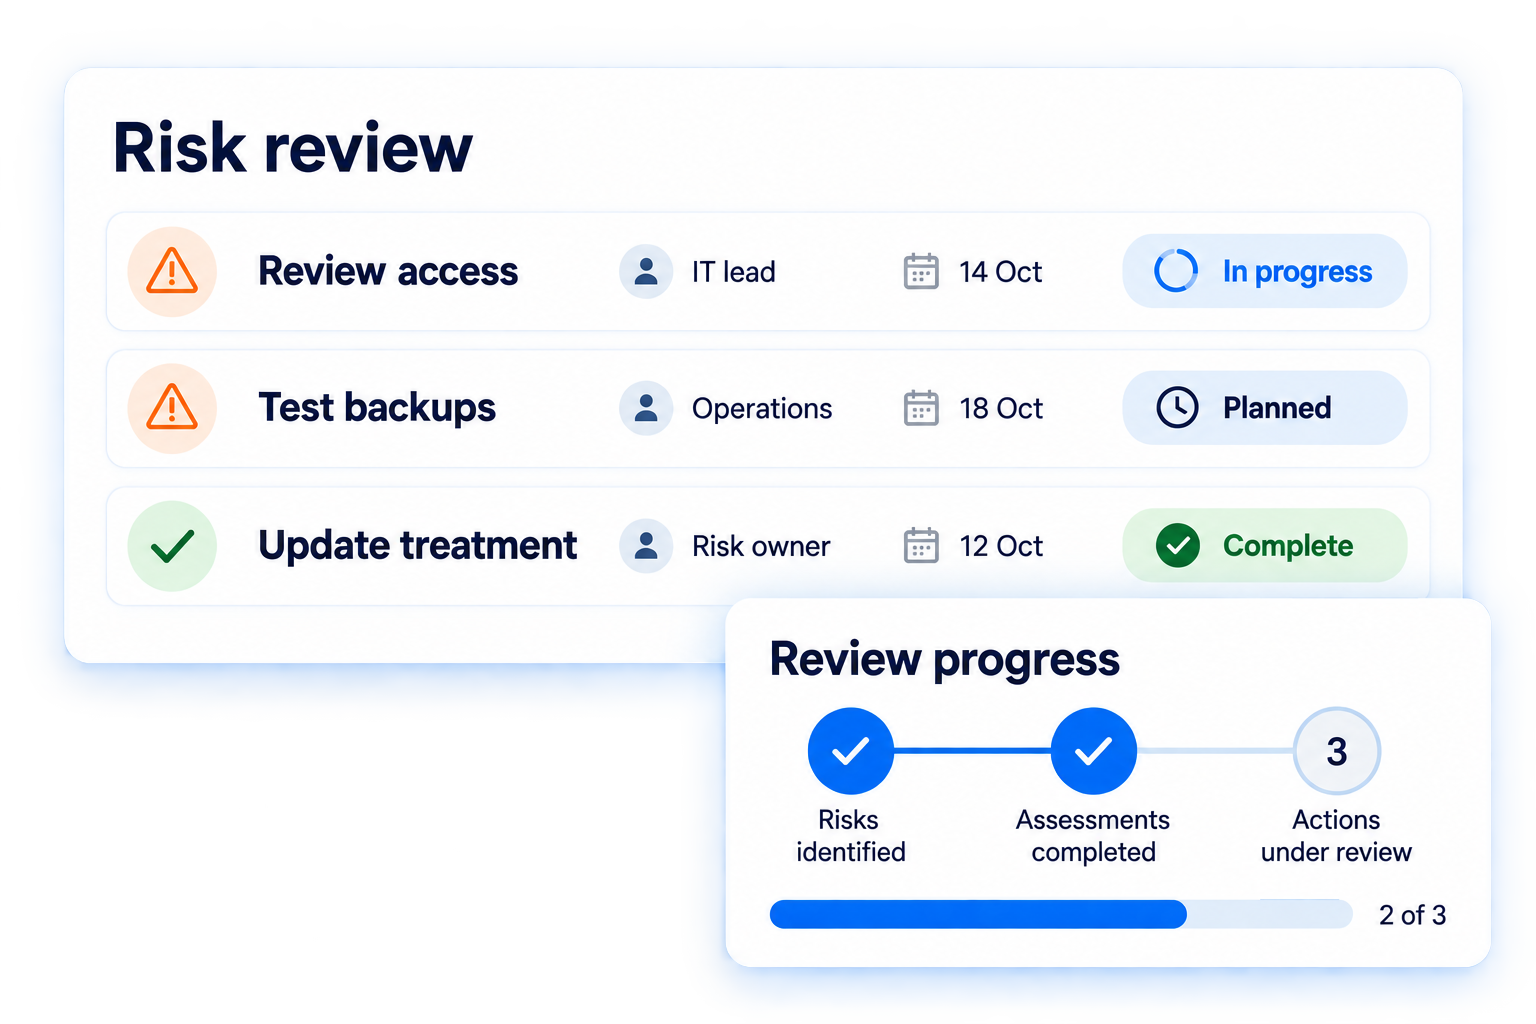
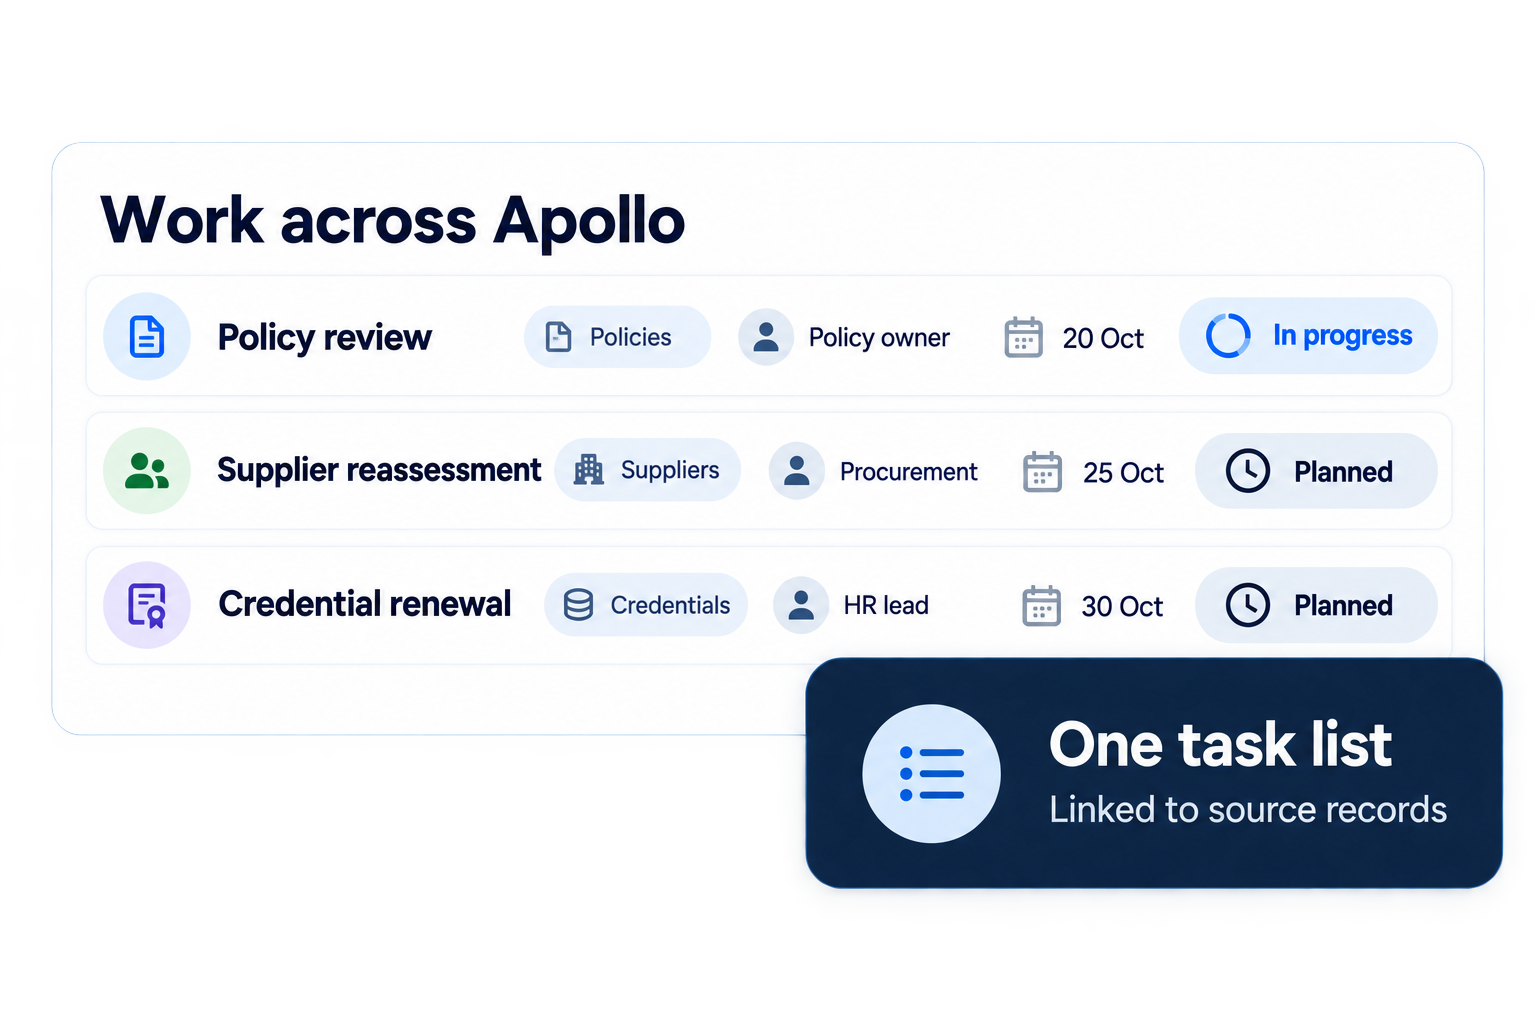
Assign, prioritise and track responsibilities across all aspects of your GRC program.
- One-off tasks
- Recurring work
- Boards and calendars
Capability
Assign, prioritise and track responsibilities across all aspects of your GRC program.
The outcome
Give every governance action a clear owner, due date and visible path to completion.
How it helps
This capability connects with the wider Apollo platform, so information can support action, evidence and reporting without being entered again.
Feature 1
Assign, prioritise and track responsibilities across all aspects of your GRC program.
Feature 2
Use the same people, records and supporting context across Apollo instead of recreating it for each area of work.
Feature 3
This shared capability supports every Apollo bundle and works alongside the specialised capabilities your team uses.
What is included
Use the capability you need now while keeping its records, work and evidence ready for related capabilities across Apollo.
Included features
Connected platform
See where this capability is available and the related capabilities and solutions that use the same connected information.
Keep owners, comments, decisions, due dates and progress visible alongside the work.
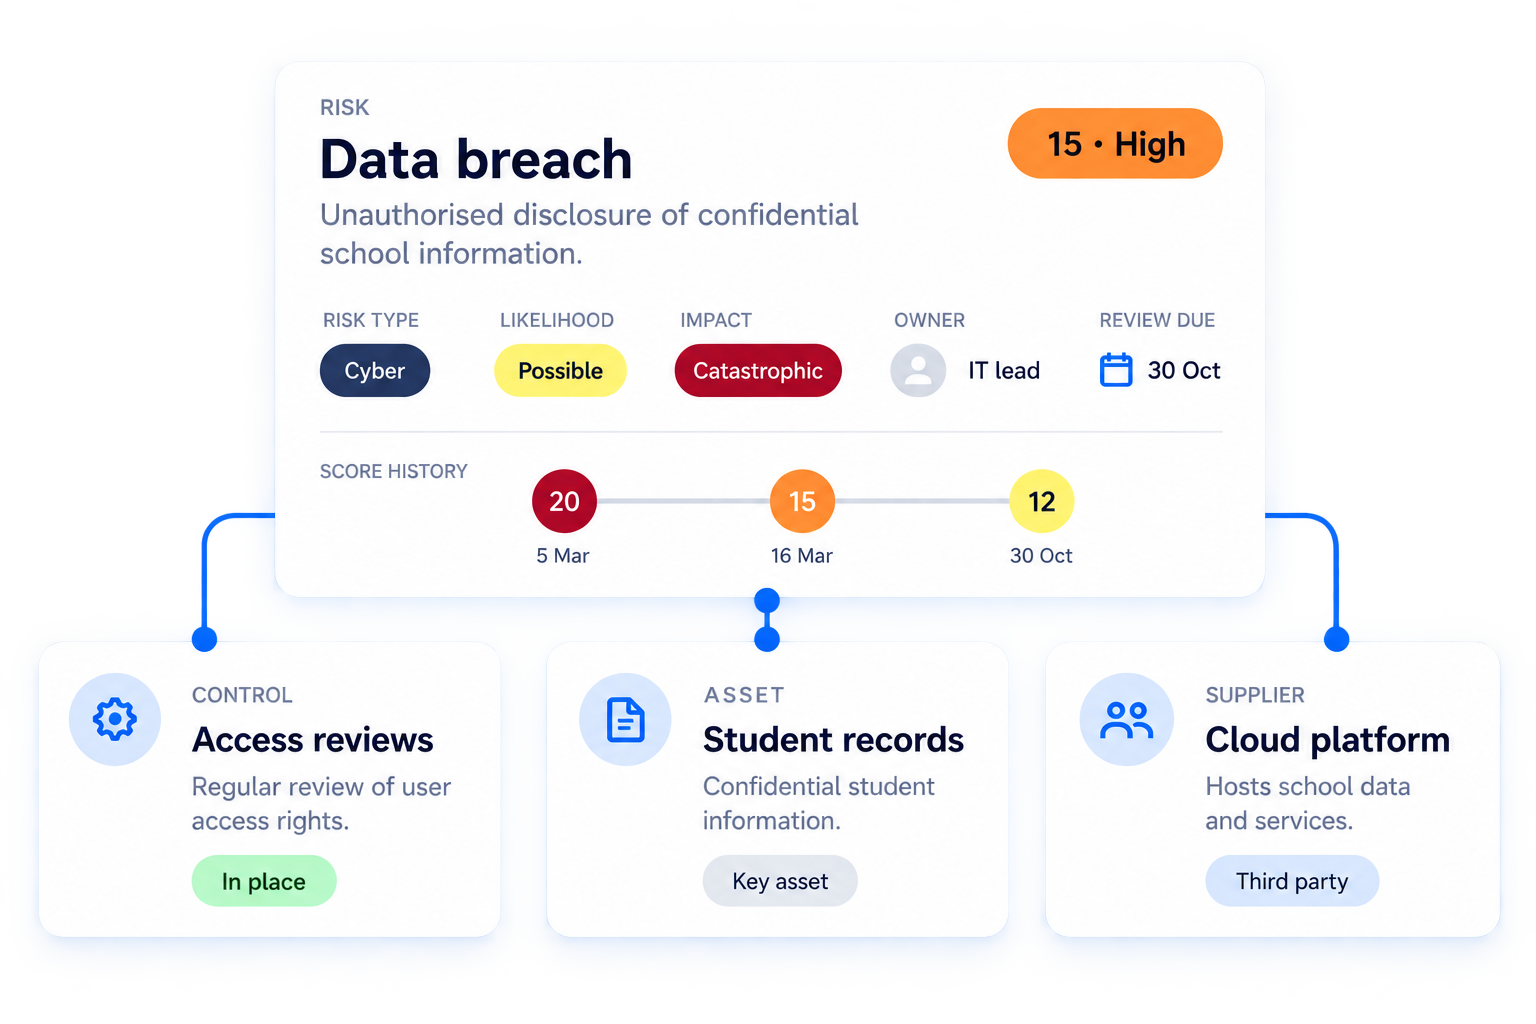
Explore capabilityConnect risks, obligations, controls, assets, suppliers, policies and work without rebuilding the same context.
Explore capabilityProduct
Use risk management software to maintain connected registers for risks, controls, assets and suppliers, so decisions are based on current information rather than separate spreadsheets.
Explore productProduct
Use compliance management software to turn frameworks and obligations into active projects with owned responses, linked controls, evidence and follow-up work.
Explore productProduct
Create guided forms and turn submissions into clear, repeatable workflows. Route requests, reviews and reports through assigned tasks, decisions and outcomes, with the information your team needs at each step.
Explore productProduct
Run supplier assessments automatically, with AI keeping supplier details and assessments up to date. Add your organisation's usage and data-handling context to understand what each supplier means for you.
Explore productProduct
Run realistic, authorised phishing exercises that help staff recognise common techniques and learn safely from mistakes.
Explore productProduct
Monitor whether staff credentials have appeared in known data breaches and prompt practical follow-up when exposure is identified.
Explore productProduct
Manage the checks, clearances, qualifications, registrations and training staff need for their roles.
Explore productProduct
Authorise sites, run security scans and manage the findings through to practical remediation.
Explore productCustomer proof
See how customers use this capability as part of a broader security, governance or compliance outcome.
Questions and answers
Practical answers to common questions about managing this responsibility well.
Give every governance action a clear owner, due date and visible path to completion.
It should cover one-off tasks, recurring work, boards and calendars, ownership and priorities and comments and activity, with enough context to support action and explain decisions.
Ownership should sit with the person who can make decisions and keep the information current. A specialist or governance team may provide the method, but accountability should not be left with an unnamed group.
Set review dates according to risk and reassess after relevant incidents, material change, new evidence or overdue follow-up work. Preserve the history so changes remain explainable.
Keep the source information, owner, review and approval history, supporting documents and resulting actions needed to show what was considered and what happened next.
Book a focused demonstration and we will show how the capability fits your current responsibilities, existing information and next practical priorities.