1
Understand the supplier
Start with available supplier information and record the service, contract, data and business owner.
Solution
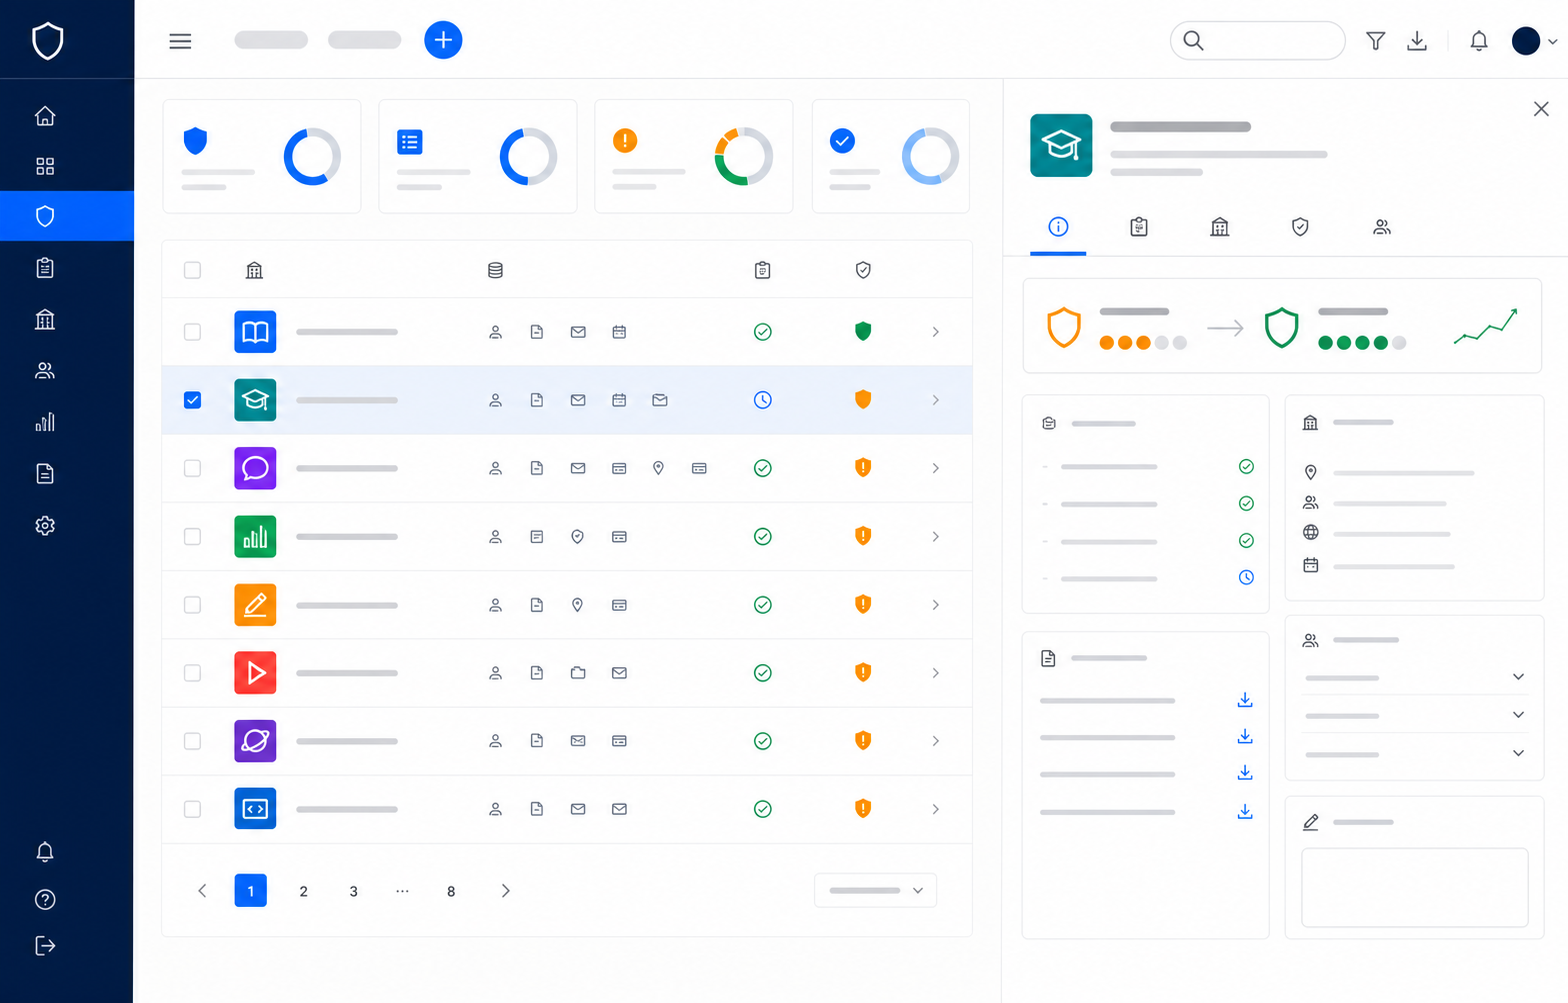
Help IT, procurement and operations teams assess digital suppliers, add school-specific context and focus deeper review where the risk is greatest.
The problem
You are asked whether a supplier is safe, but technical claims, privacy terms, contracts and the school’s actual use are difficult to assess together.
Schools should not have to repeat the same baseline investigation—or accept unknown risk—to adopt useful technology.
A clearer way forward
Apollo Secure runs supplier assessments automatically and uses AI to keep supplier details and assessments current. Schools add their own data and usage context and focus deeper review where it matters.
Trusted in education
Apollo Secure works with education industry bodies to ensure we're building the best Edtech solution for Australian schools.
A simple plan
Start from the position you have today and build a repeatable rhythm your team can maintain.
Start with available supplier information and record the service, contract, data and business owner.
Apply school-specific context to identify privacy, security, continuity and concentration risks.
Record the decision, assign required actions and review important suppliers as circumstances change.
Connected in Apollo
Apollo connects these capabilities so records, ownership, evidence and reporting remain in one place.
Evaluate supplier data, compliance and contractual evidence in the context of how the organisation uses the service.
Explore capabilityMaintain the third parties the organisation relies on, their services, data context, ownership and review status.
Explore capability
The outcome
Procurement, technology and privacy teams work from the same facts and can show why a supplier was approved, restricted or needs action.
Questions and answers
Practical answers to common questions about managing this responsibility well.
Start with the service's access to student and staff information, integrations, criticality and impact of disruption. Then assess privacy, security, contractual, continuity and subprocessor risks in proportion to that exposure.
Every supplier should be triaged, but not every one needs the same depth of review. Tools handling sensitive data, authenticating users, integrating with core systems or supporting critical operations warrant deeper due diligence.
Ask what data is collected, why it is needed, where it is stored, who can access it, which subprocessors are involved, how long it is retained and how incidents, deletion and rights requests are handled.
Approval should involve the service owner and the people accountable for technology, privacy, procurement and risk in proportion to the exposure. High-risk or exceptional decisions may require executive approval.
See how Apollo Secure can help your team replace scattered work with a clear, repeatable approach.