How should organisations manage customer security assurance?+
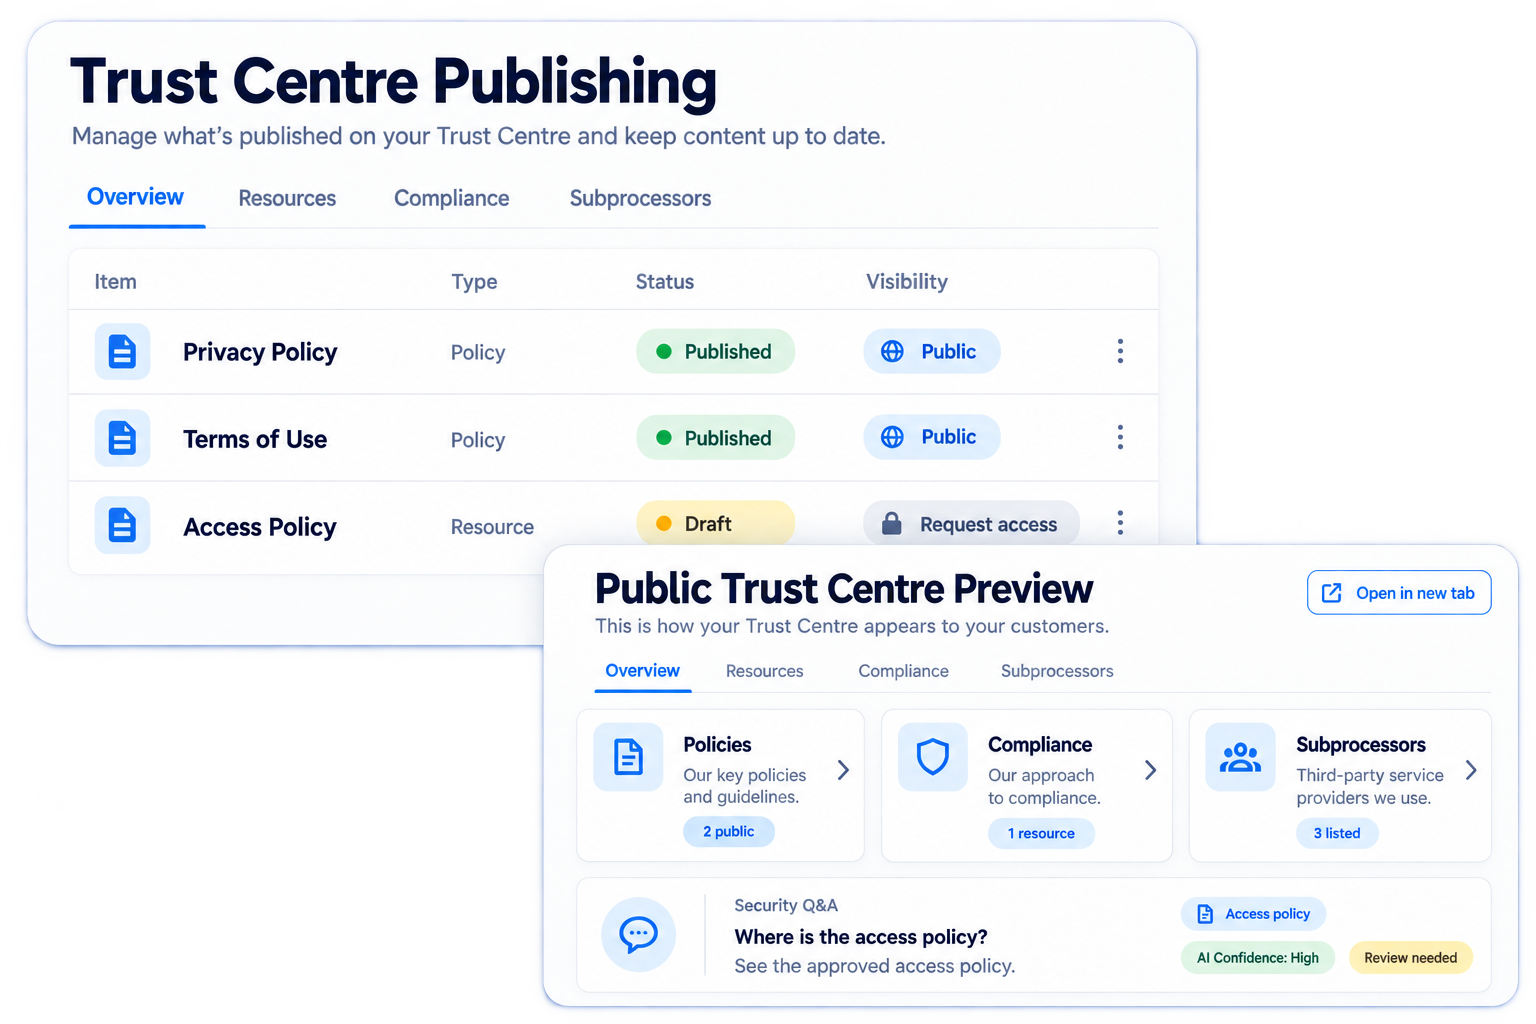
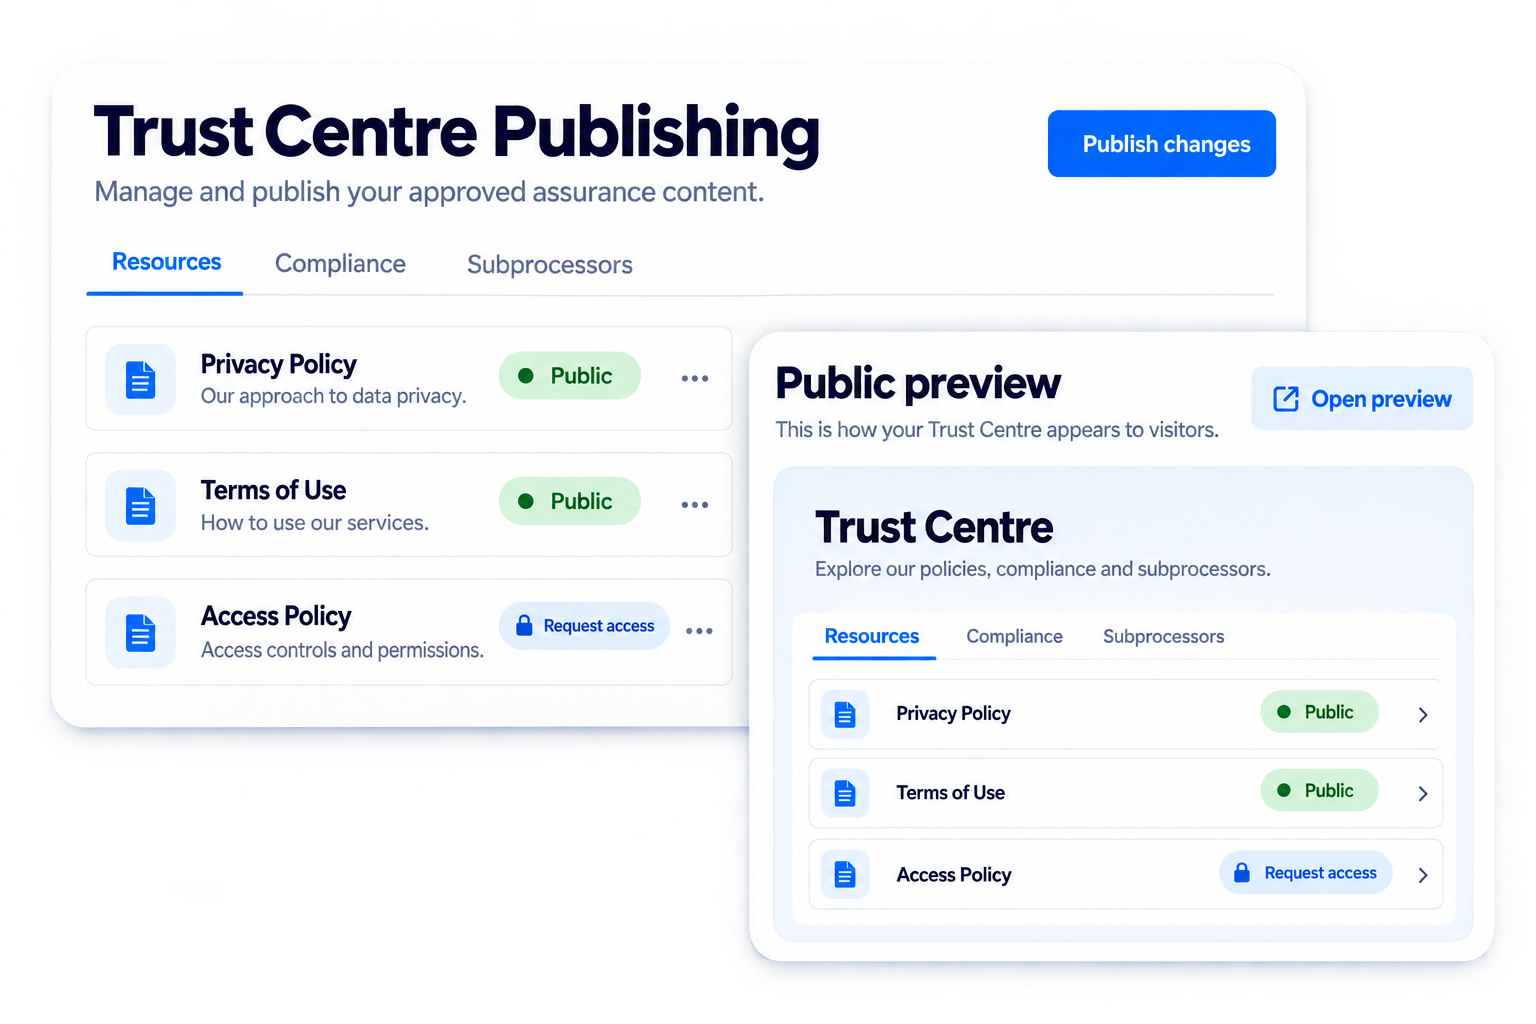
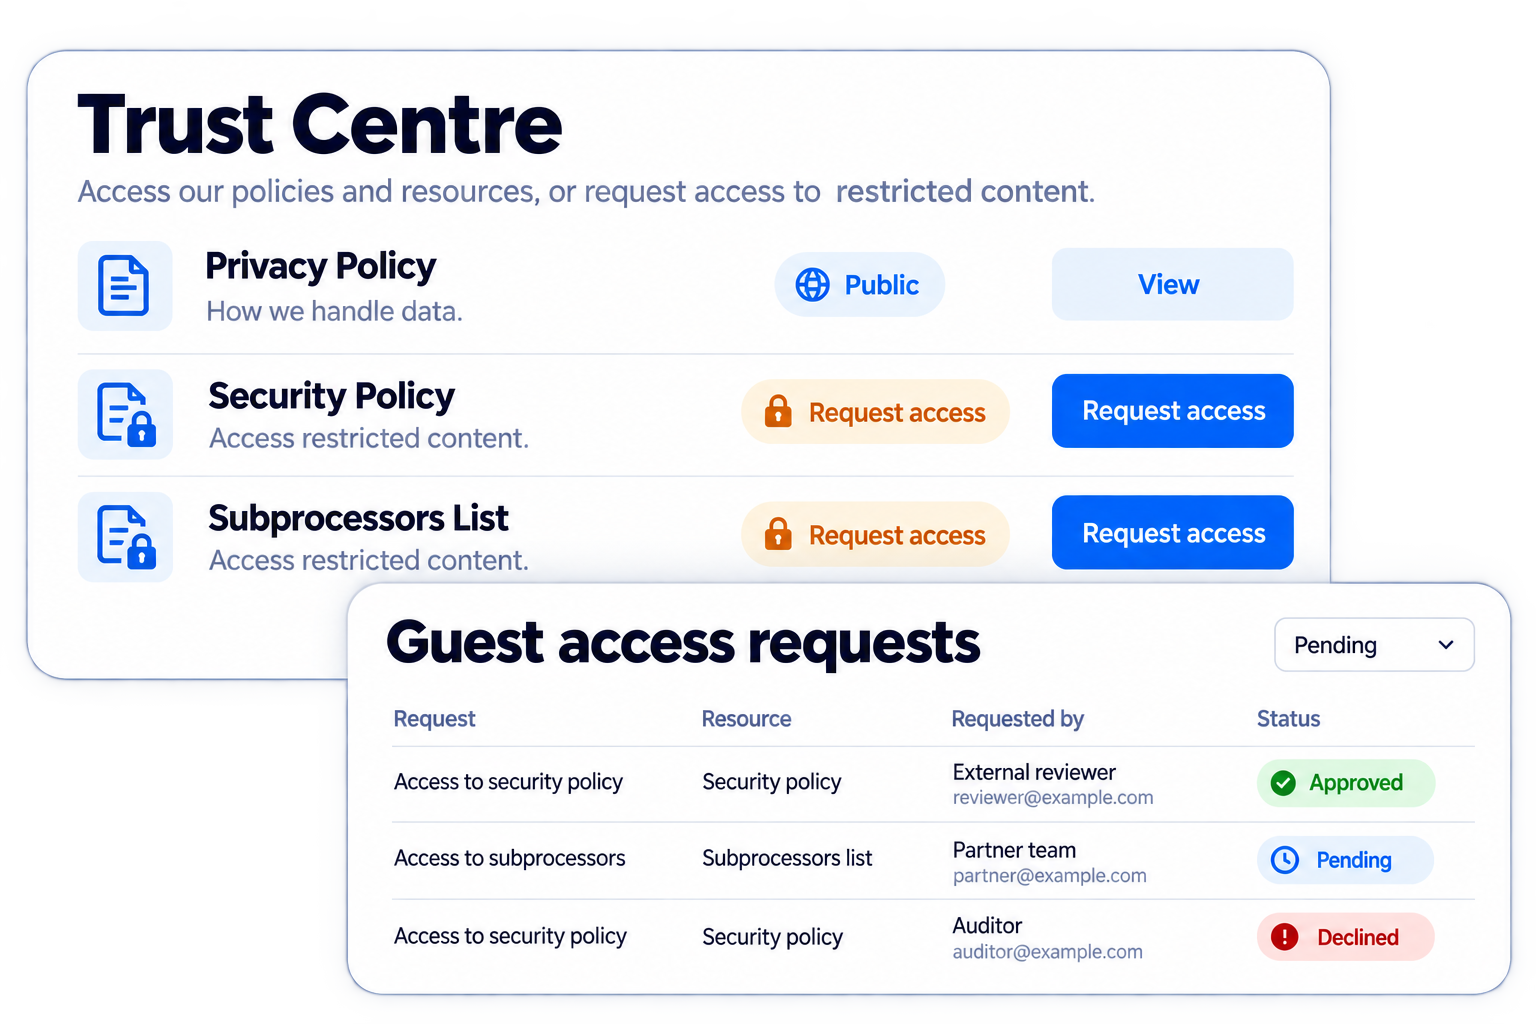
Publish approved security, privacy and compliance information through a branded customer-facing site. Give customers and partners a reliable place to find assurance information before they send another questionnaire.
What should a good process for customer security assurance include?+
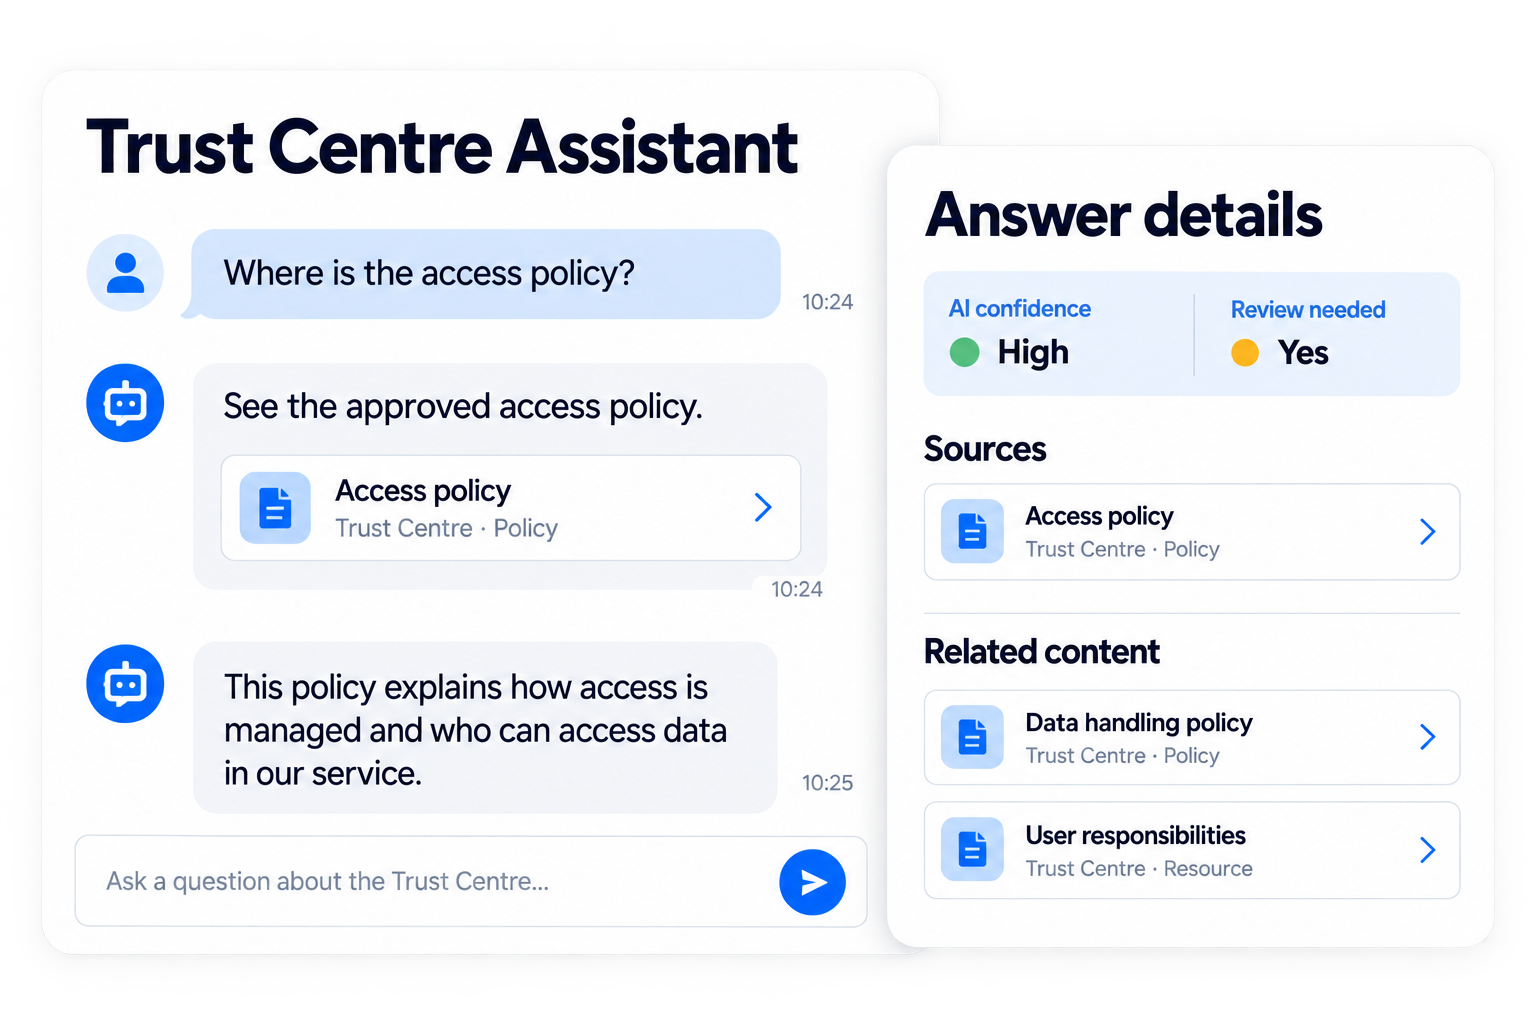
It should cover Branded assurance site, Privacy resources, Compliance disclosures, Subprocessor directory and Self-service knowledge assistant, with clear ownership, review and evidence rather than disconnected activity.
Who should be accountable for customer security assurance?+
Ownership should sit with the person who can make decisions, allocate resources and keep the work current. A governance or specialist team may coordinate the process, but material records and actions need named accountable owners.
How often should customer security assurance be reviewed?+
Use scheduled reviews based on risk and trigger an earlier reassessment after relevant incidents, regulatory change, audit findings or material changes to systems, suppliers or operating conditions.
What evidence should be retained for customer security assurance?+
Retain the source information, owner, review and approval history, supporting documents and actions needed to explain what was known, what was decided and what happened next. Relevant records include trust centre publishing, artefact library, subprocessor directory and trust centre assistant.