What makes a cyber security policy useful?+
A useful policy states the expected behaviour, scope, responsibilities and review arrangements in language its audience can follow. It should reflect the organisation's operating environment and connect to practical procedures rather than remain a generic statement of intent.
Who should review and approve IT security policies?+
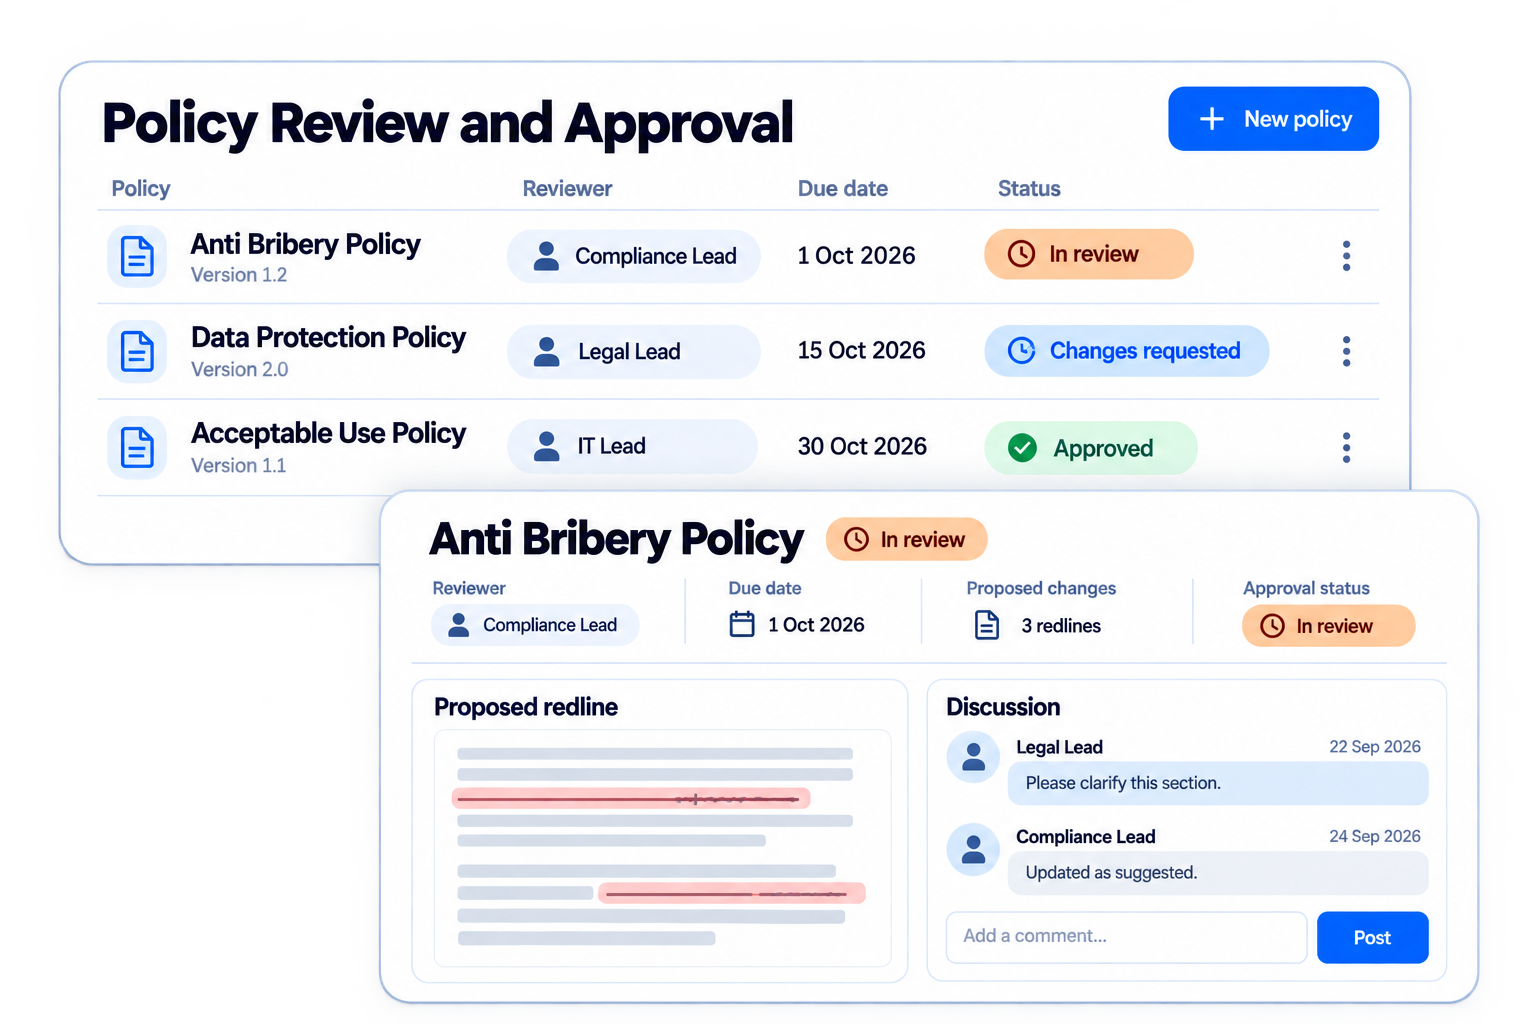
Include people who understand the technical controls and the responsibilities the policy creates. Give approval to the appropriate accountable authority under the organisation's governance arrangements, and keep the decision and effective version traceable.
When should a security policy be reviewed?+
Set a review schedule appropriate to the policy's risk and purpose. Review sooner when material system changes, incidents or changes in responsibilities show that the current wording no longer reflects the intended approach.
Does staff acknowledgement prove a security policy is followed?+
Acknowledgement records that staff have acknowledged a policy; it does not establish that the policy is understood or that a security control is effective. Use appropriate training, supervision and operational evidence alongside acknowledgements.
How should old and revised security policies be handled?+
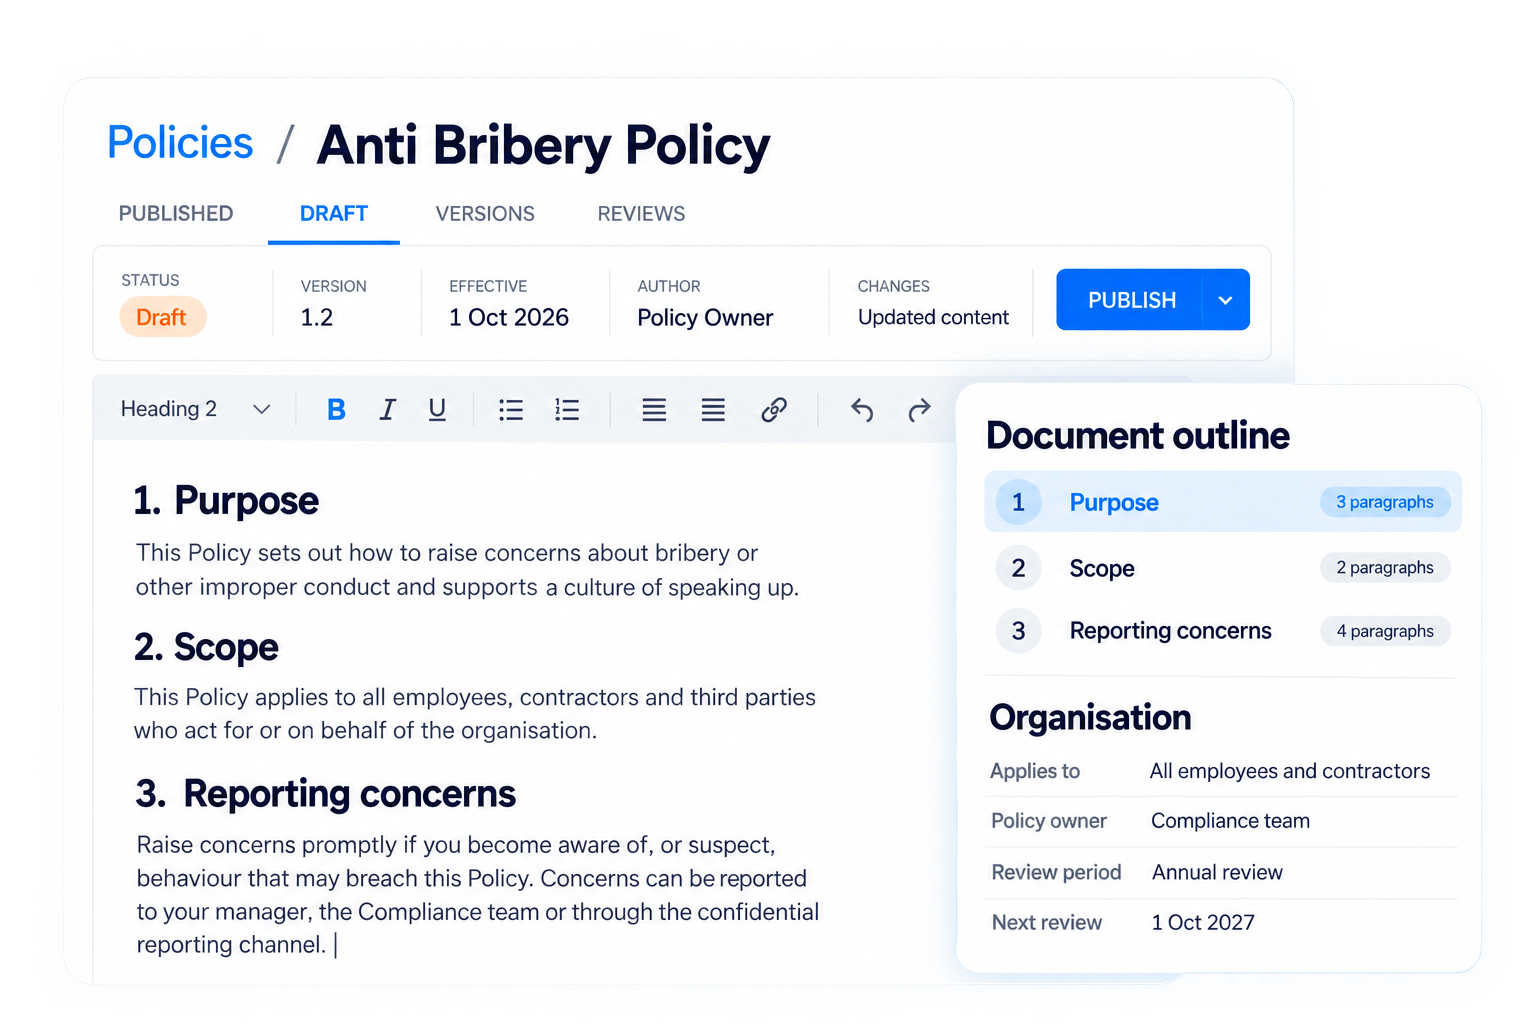
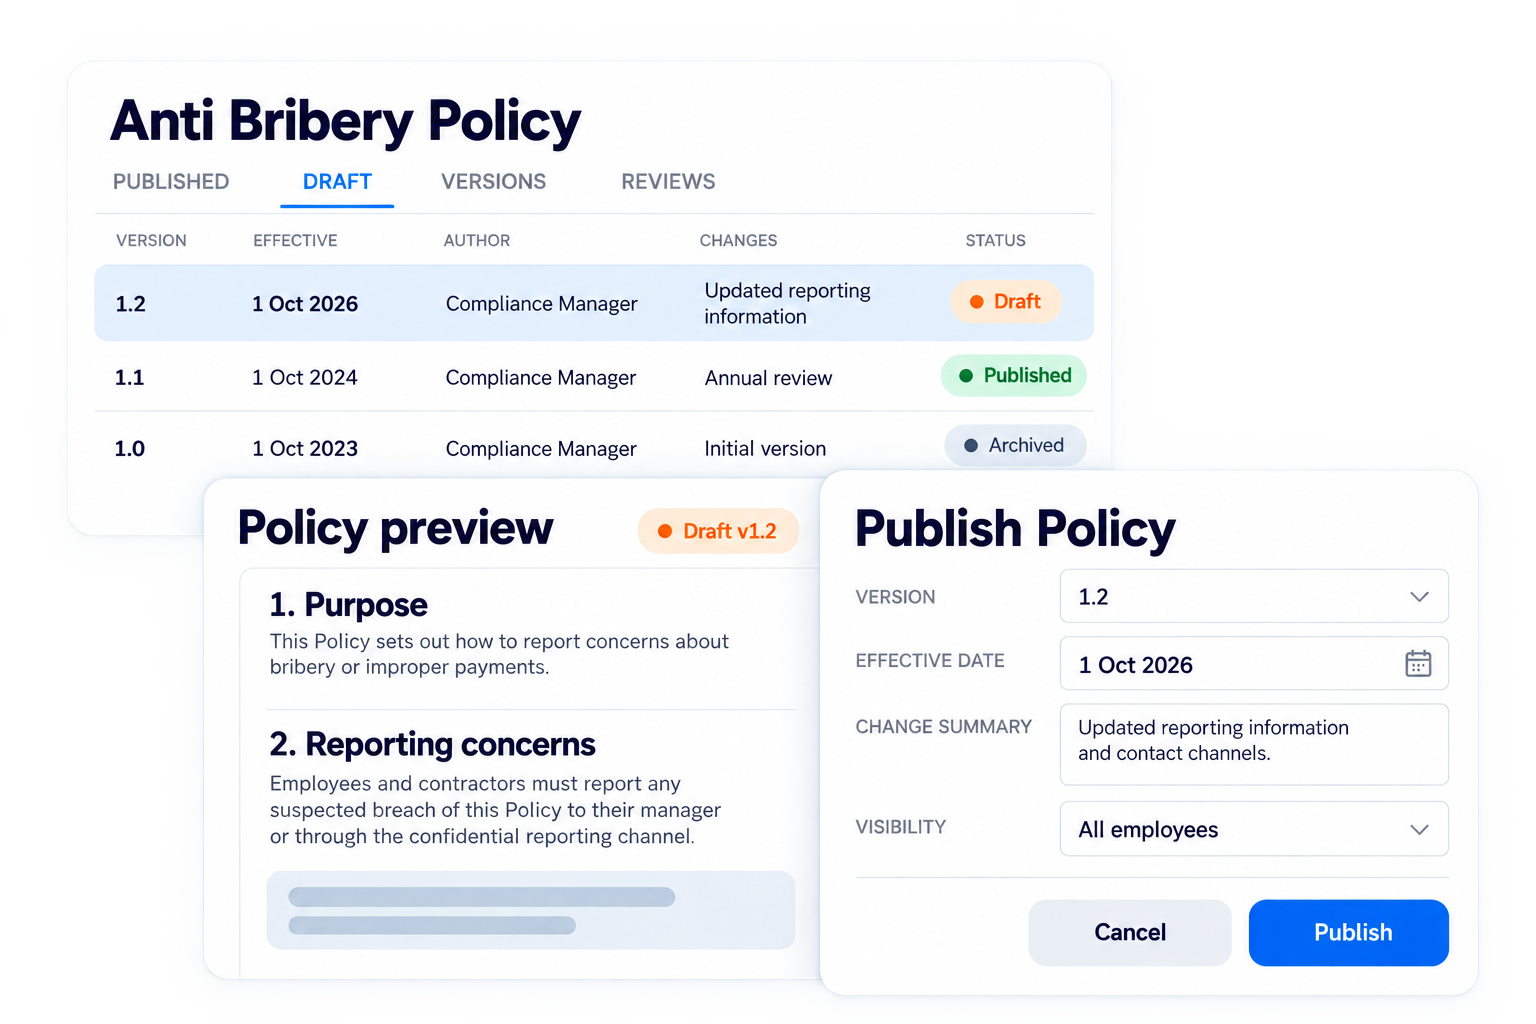
Keep proposed changes separate from the effective version, review and approve them before publication, and make the current policy easy to identify. Preserve the earlier versions and decision history so the organisation can explain what applied at a particular time.