How should a cyber framework assessment be scoped?+
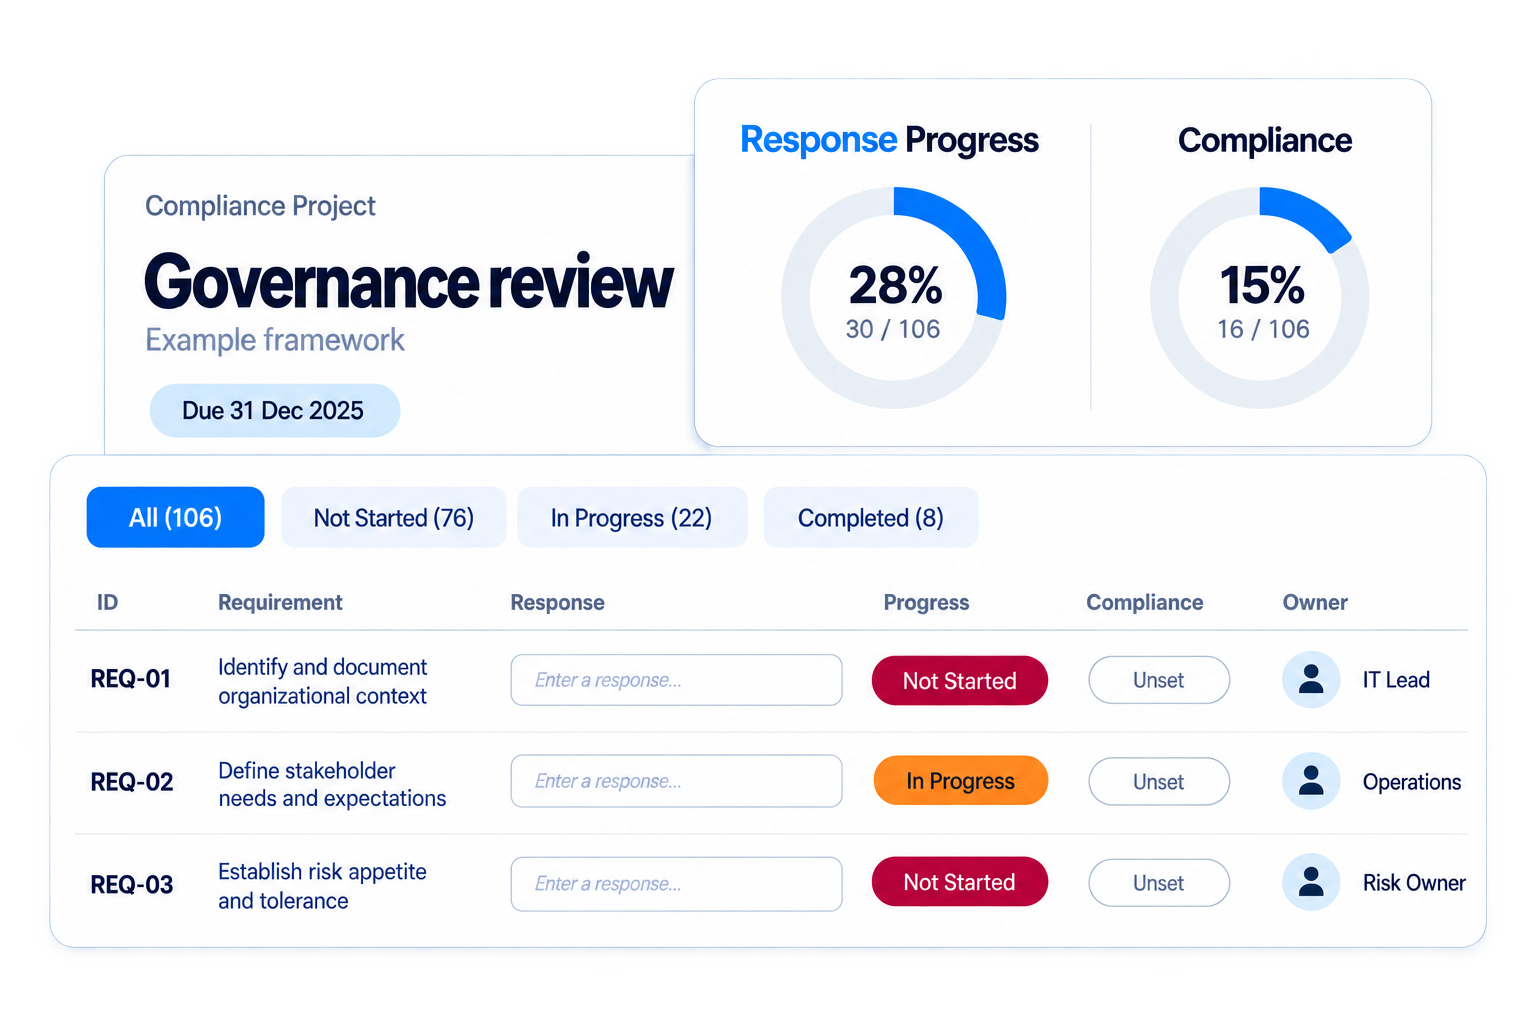
Define the systems, services, teams and assessment period before recording results. Make the framework and version explicit, and document any exclusions so readers understand what the assessment does and does not cover.
What evidence supports a cyber security assessment?+
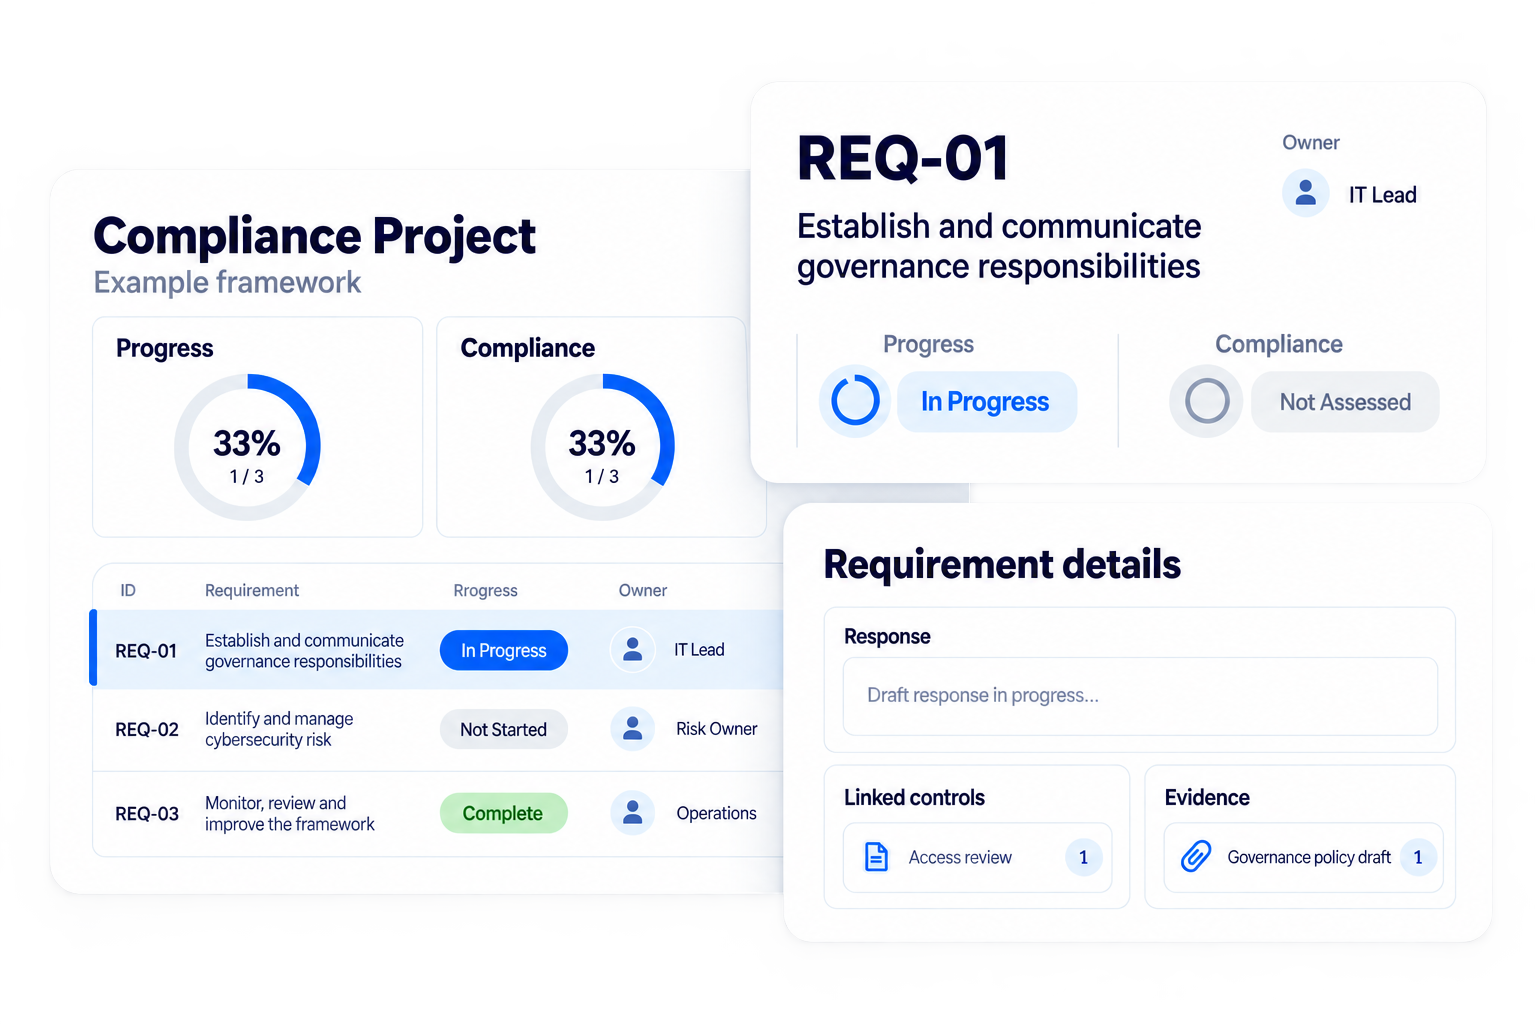
Use evidence that demonstrates how a control is implemented and operates. Configuration records, test results and review records can support an assessment; a written policy alone describes intent rather than proving effectiveness. Keep the evidence relevant to the systems and period being assessed.
How should gaps in a cyber assessment be prioritised?+
Consider the exposure each gap creates, the systems affected and the dependencies between improvements. Assign an owner and next action, and keep the remaining gap visible while work is underway rather than treating a planned action as a completed control.
Does completing a cyber checklist demonstrate compliance?+
A completed checklist alone does not demonstrate that controls are effective. Responses need a defined scope, supporting evidence and an accountable review. Any conclusion should reflect what was actually assessed rather than implying certification or universal compliance.
How can teams keep cyber assessment evidence current?+
Review evidence when controls, systems or assessment scope change, and set review dates appropriate to the risk. Retain prior assessment records so the team can explain progress without losing the basis of earlier decisions.