Feature 1
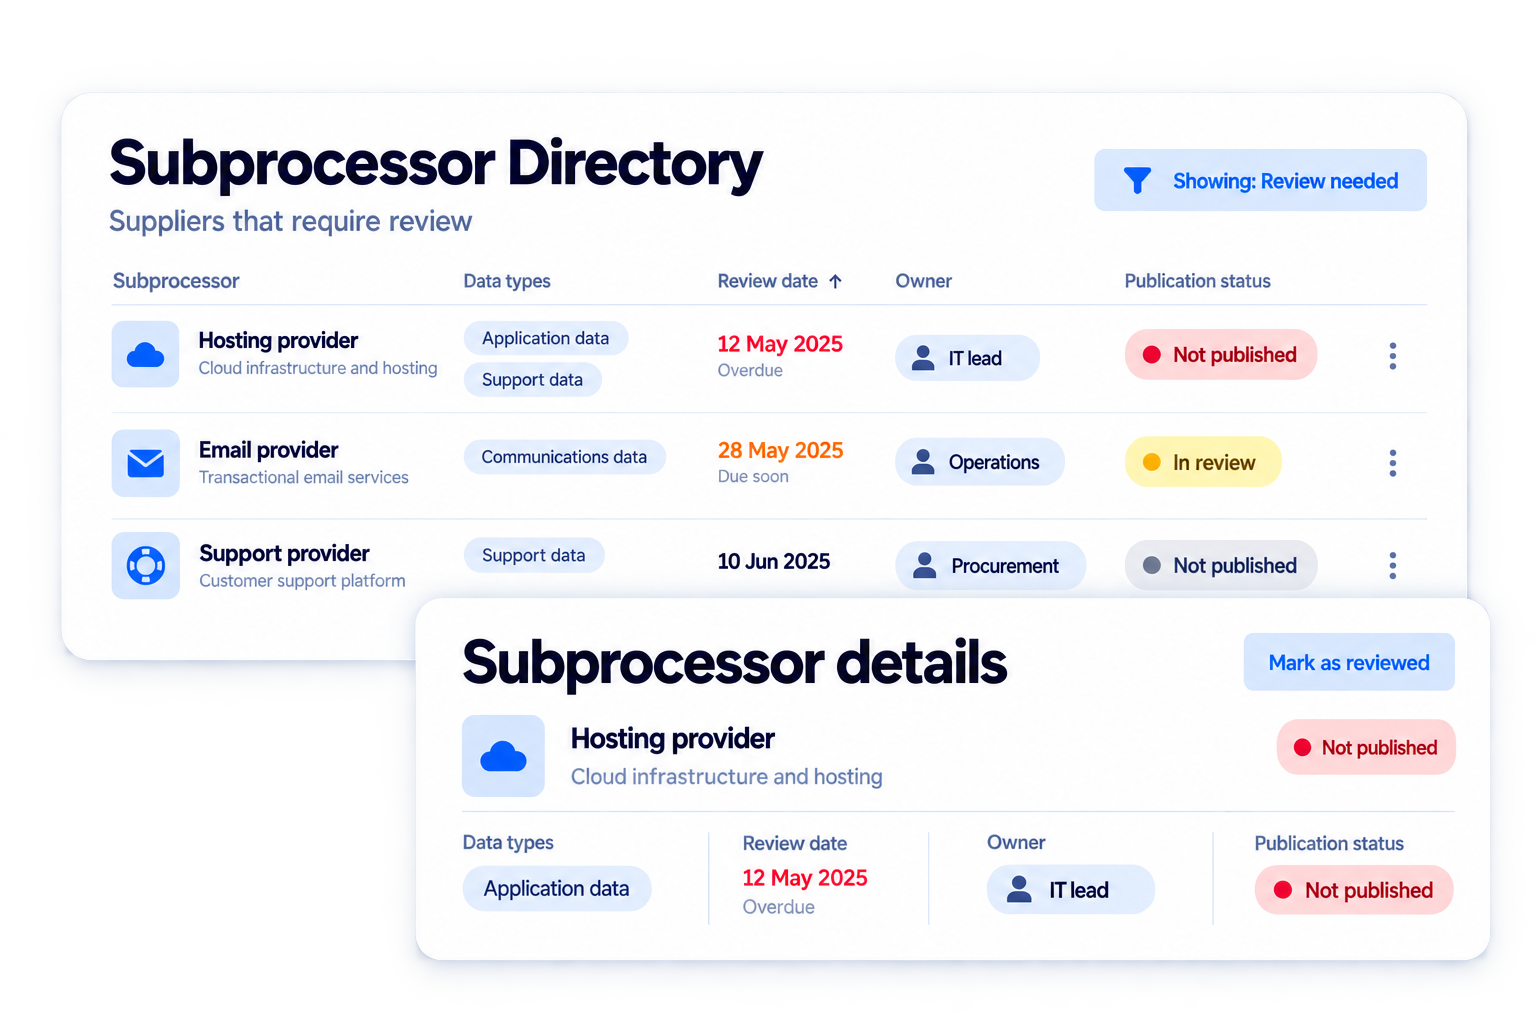
Publish a useful subprocessor directory
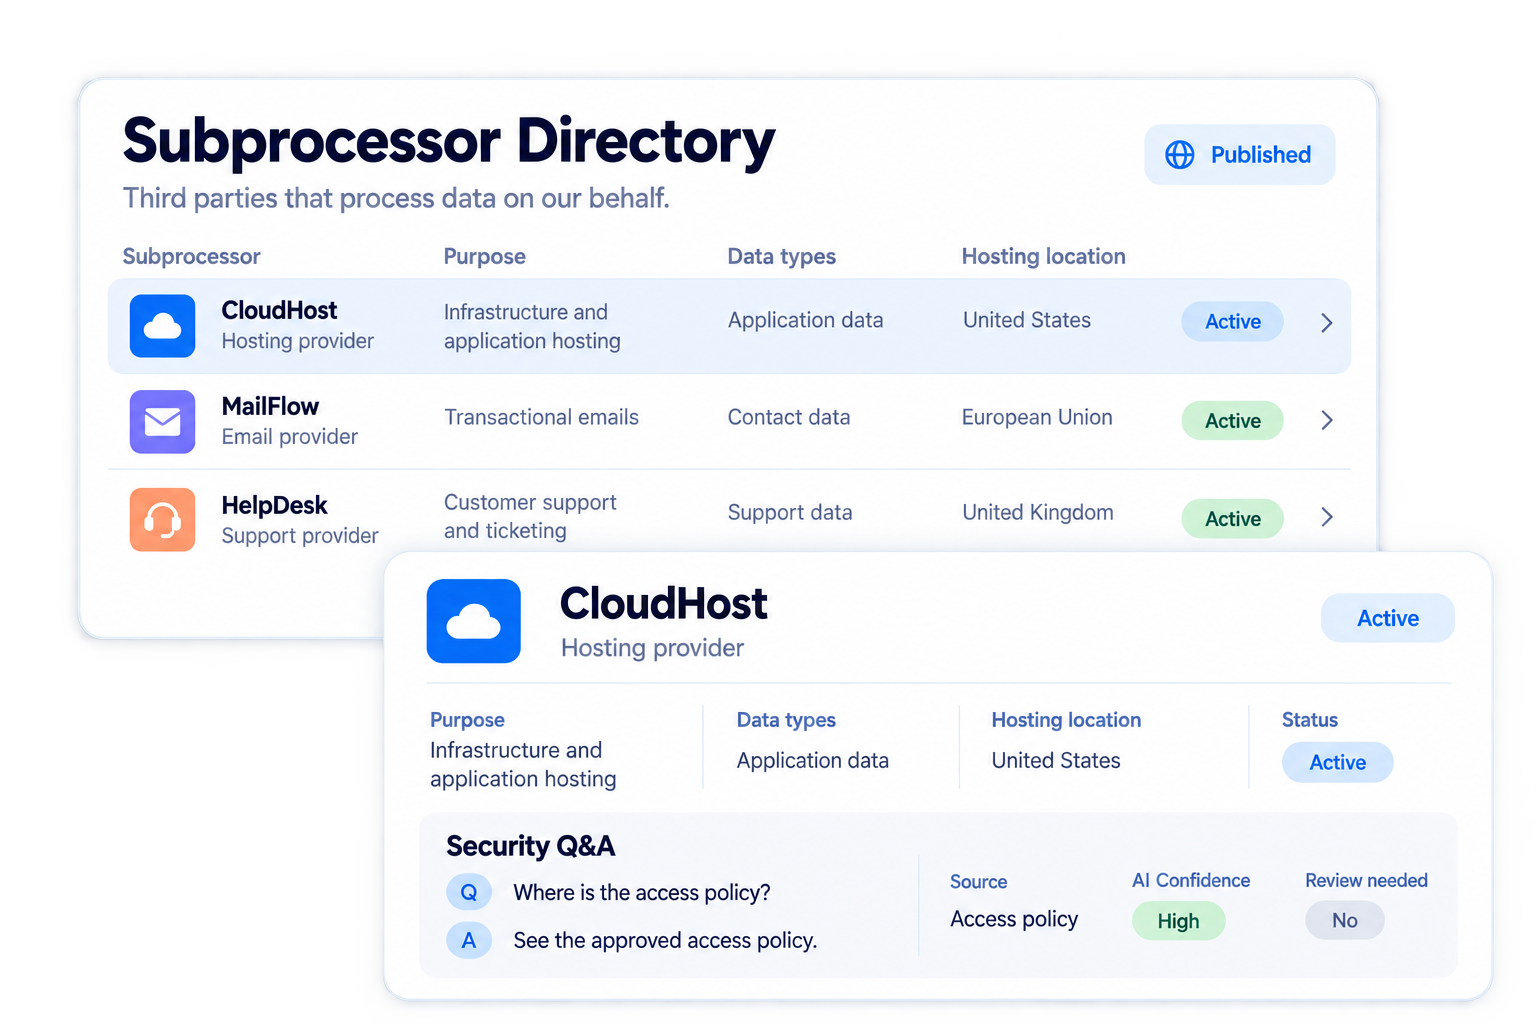
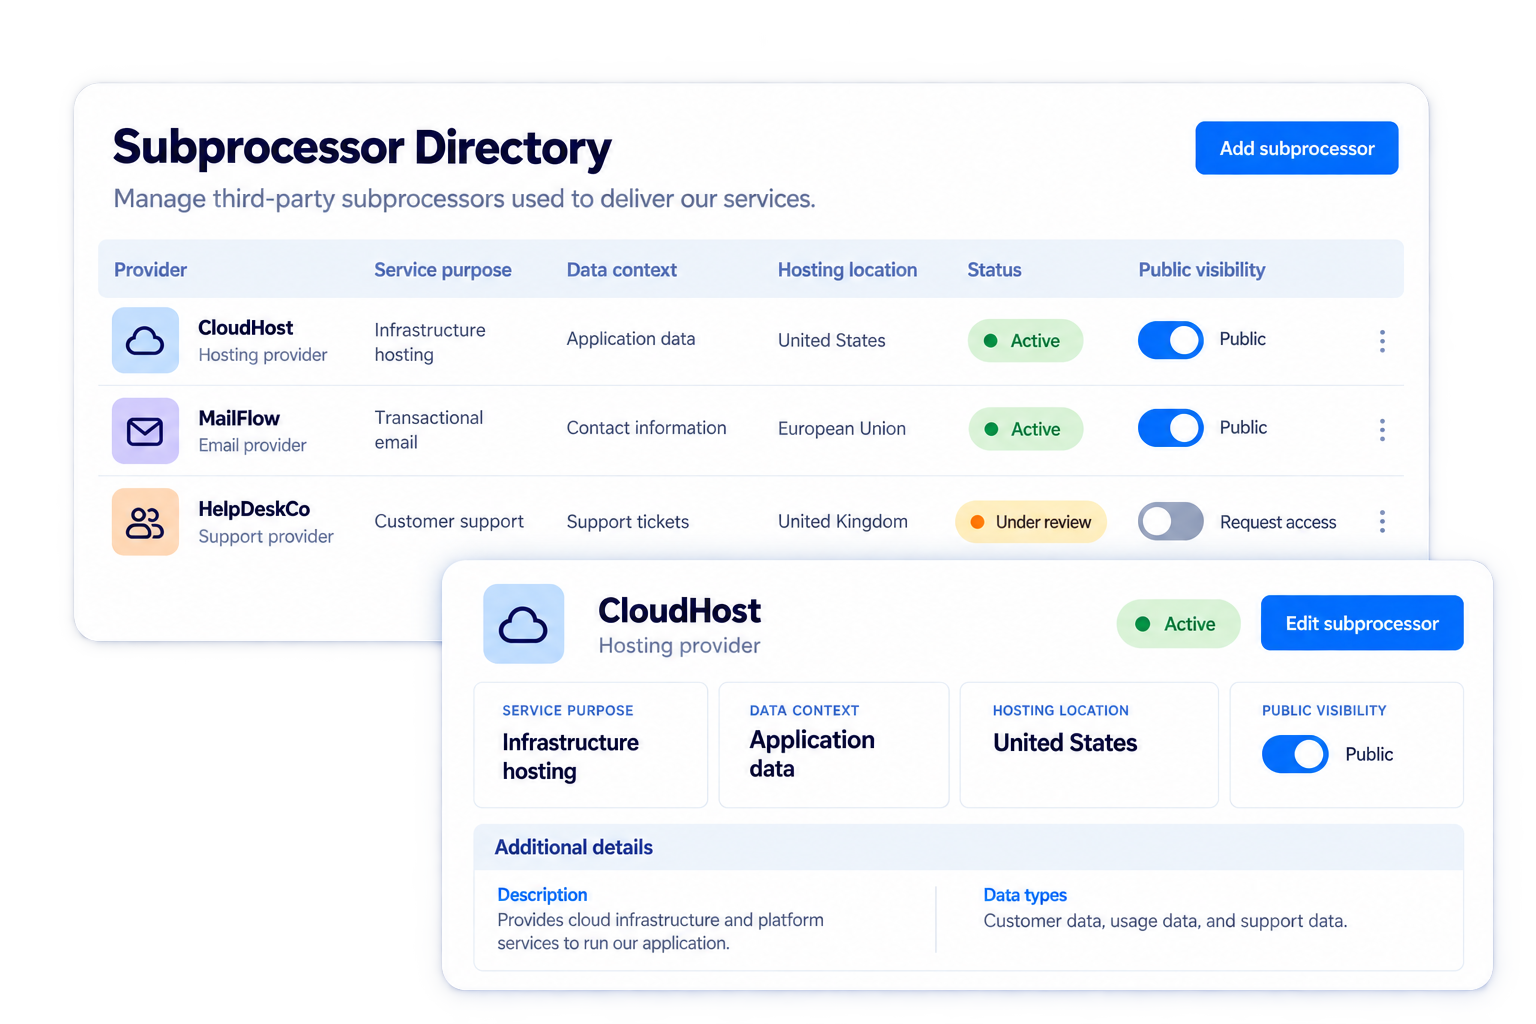
Maintain the provider context customers ask for and publish approved records directly to the Trust Centre.
- Describe the service
- Record data and location context
- Set public visibility
Capability
Maintain and publish the third parties involved in delivering your service, with the context customers need for assurance and privacy review.
The outcome
Give prospects and customers a current, transparent view of subprocessors without answering the same vendor questions repeatedly.
How it helps
This capability connects with the wider Apollo platform, so information can support action, evidence and reporting without being entered again.
Feature 1
Maintain the provider context customers ask for and publish approved records directly to the Trust Centre.
Feature 2
Review changes centrally so customer-facing information reflects the organisation's current suppliers.
What is included
Use the capability you need now while keeping its records, work and evidence ready for related capabilities across Apollo.
Included features
Connected platform
See where this capability is available and the related capabilities and solutions that use the same connected information.
Configure and publish a branded site for sharing approved security, privacy and compliance information.
Explore capabilityMaintain the third parties the organisation relies on, their services, data context, ownership and review status.
Explore capabilityQuestions and answers
Practical answers to common questions about managing this responsibility well.
Give prospects and customers a current, transparent view of subprocessors without answering the same vendor questions repeatedly.
It should cover subprocessor records, service purpose, data and hosting context, public visibility and status and review dates, with enough context to support action and explain decisions.
Ownership should sit with the person who can make decisions and keep the information current. A specialist or governance team may provide the method, but accountability should not be left with an unnamed group.
Set review dates according to risk and reassess after relevant incidents, material change, new evidence or overdue follow-up work. Preserve the history so changes remain explainable.
Keep the source information, owner, review and approval history, supporting documents and resulting actions needed to show what was considered and what happened next.
Book a focused demonstration and we will show how the capability fits your current responsibilities, existing information and next practical priorities.